AttackForge alternative
Vulnotes vs AttackForgeDesign reports visually. Pay one simple price.
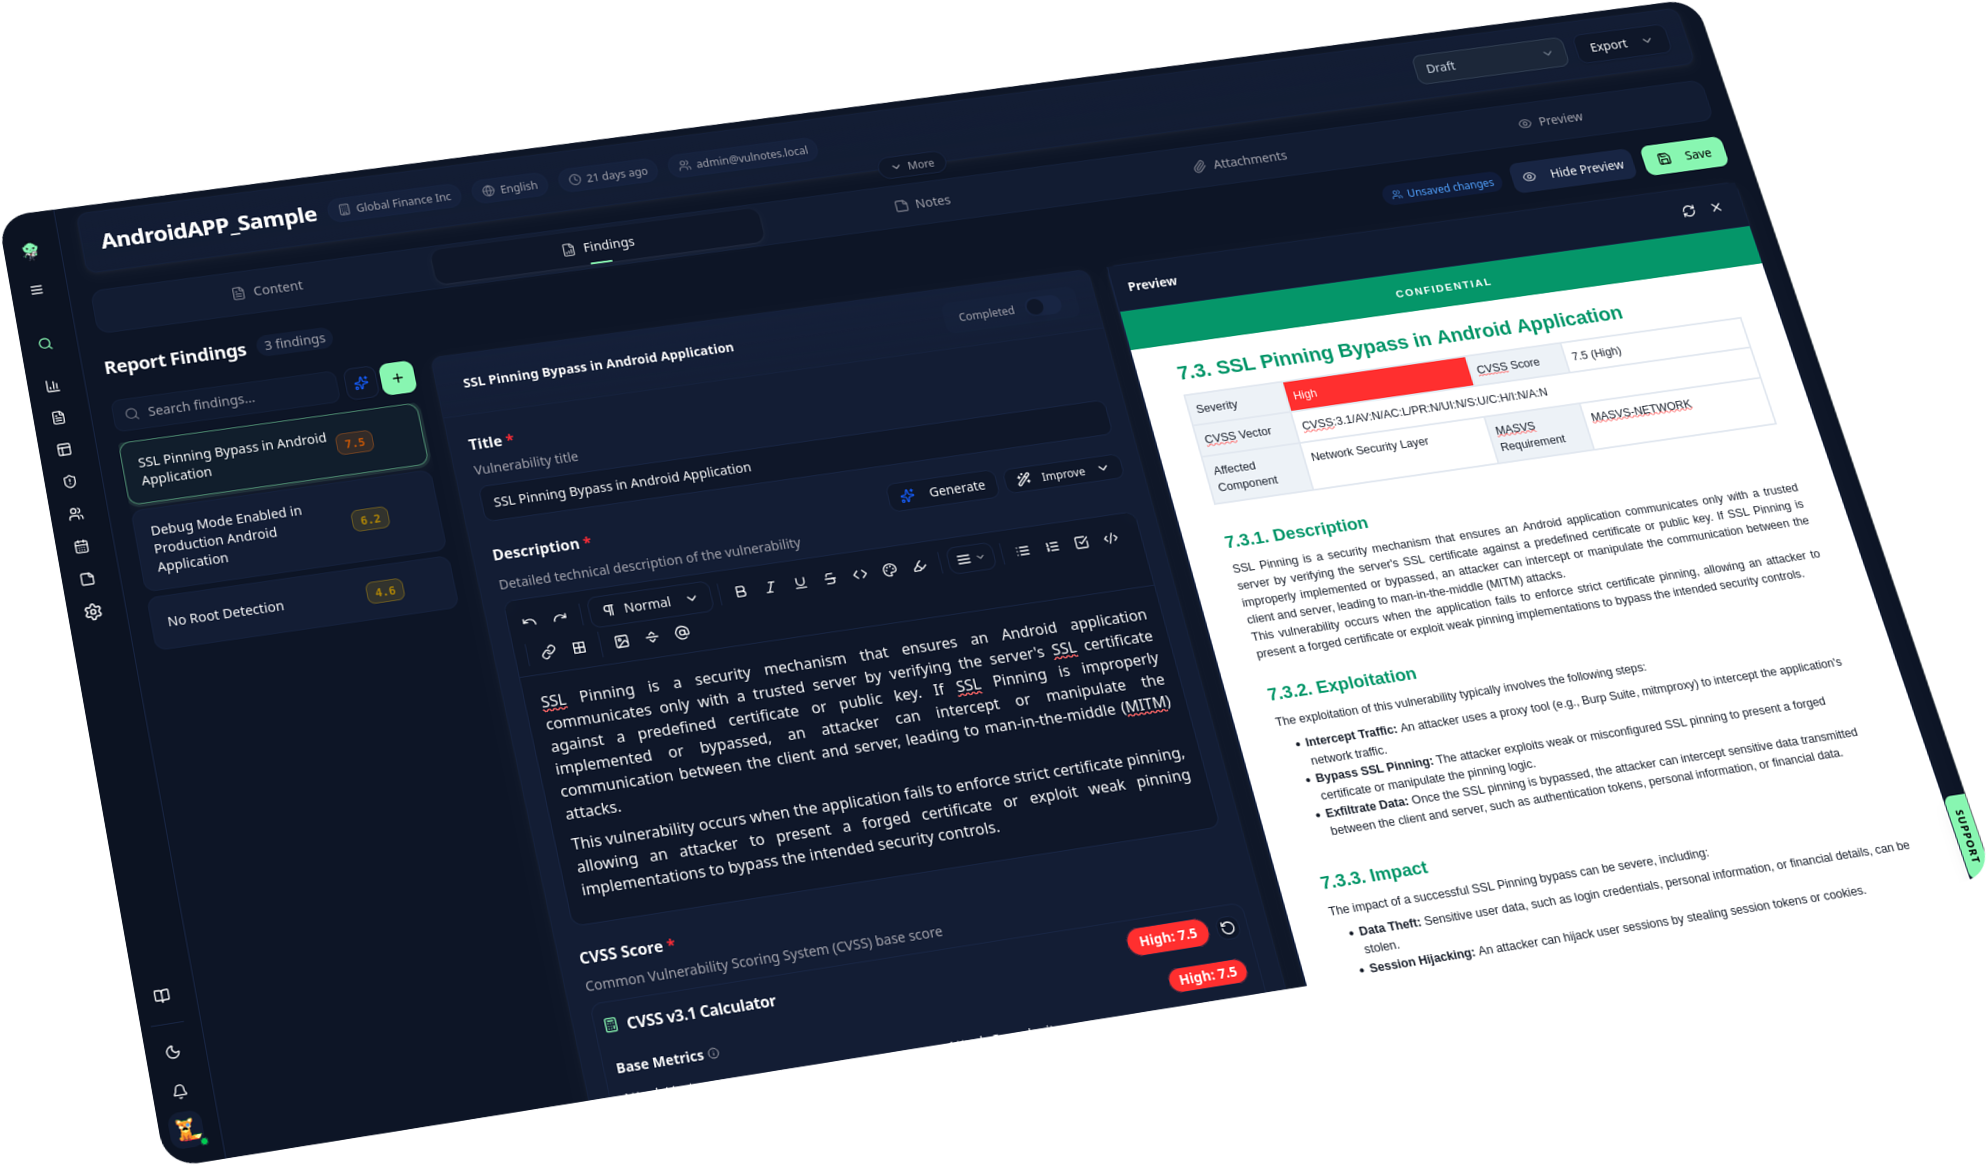
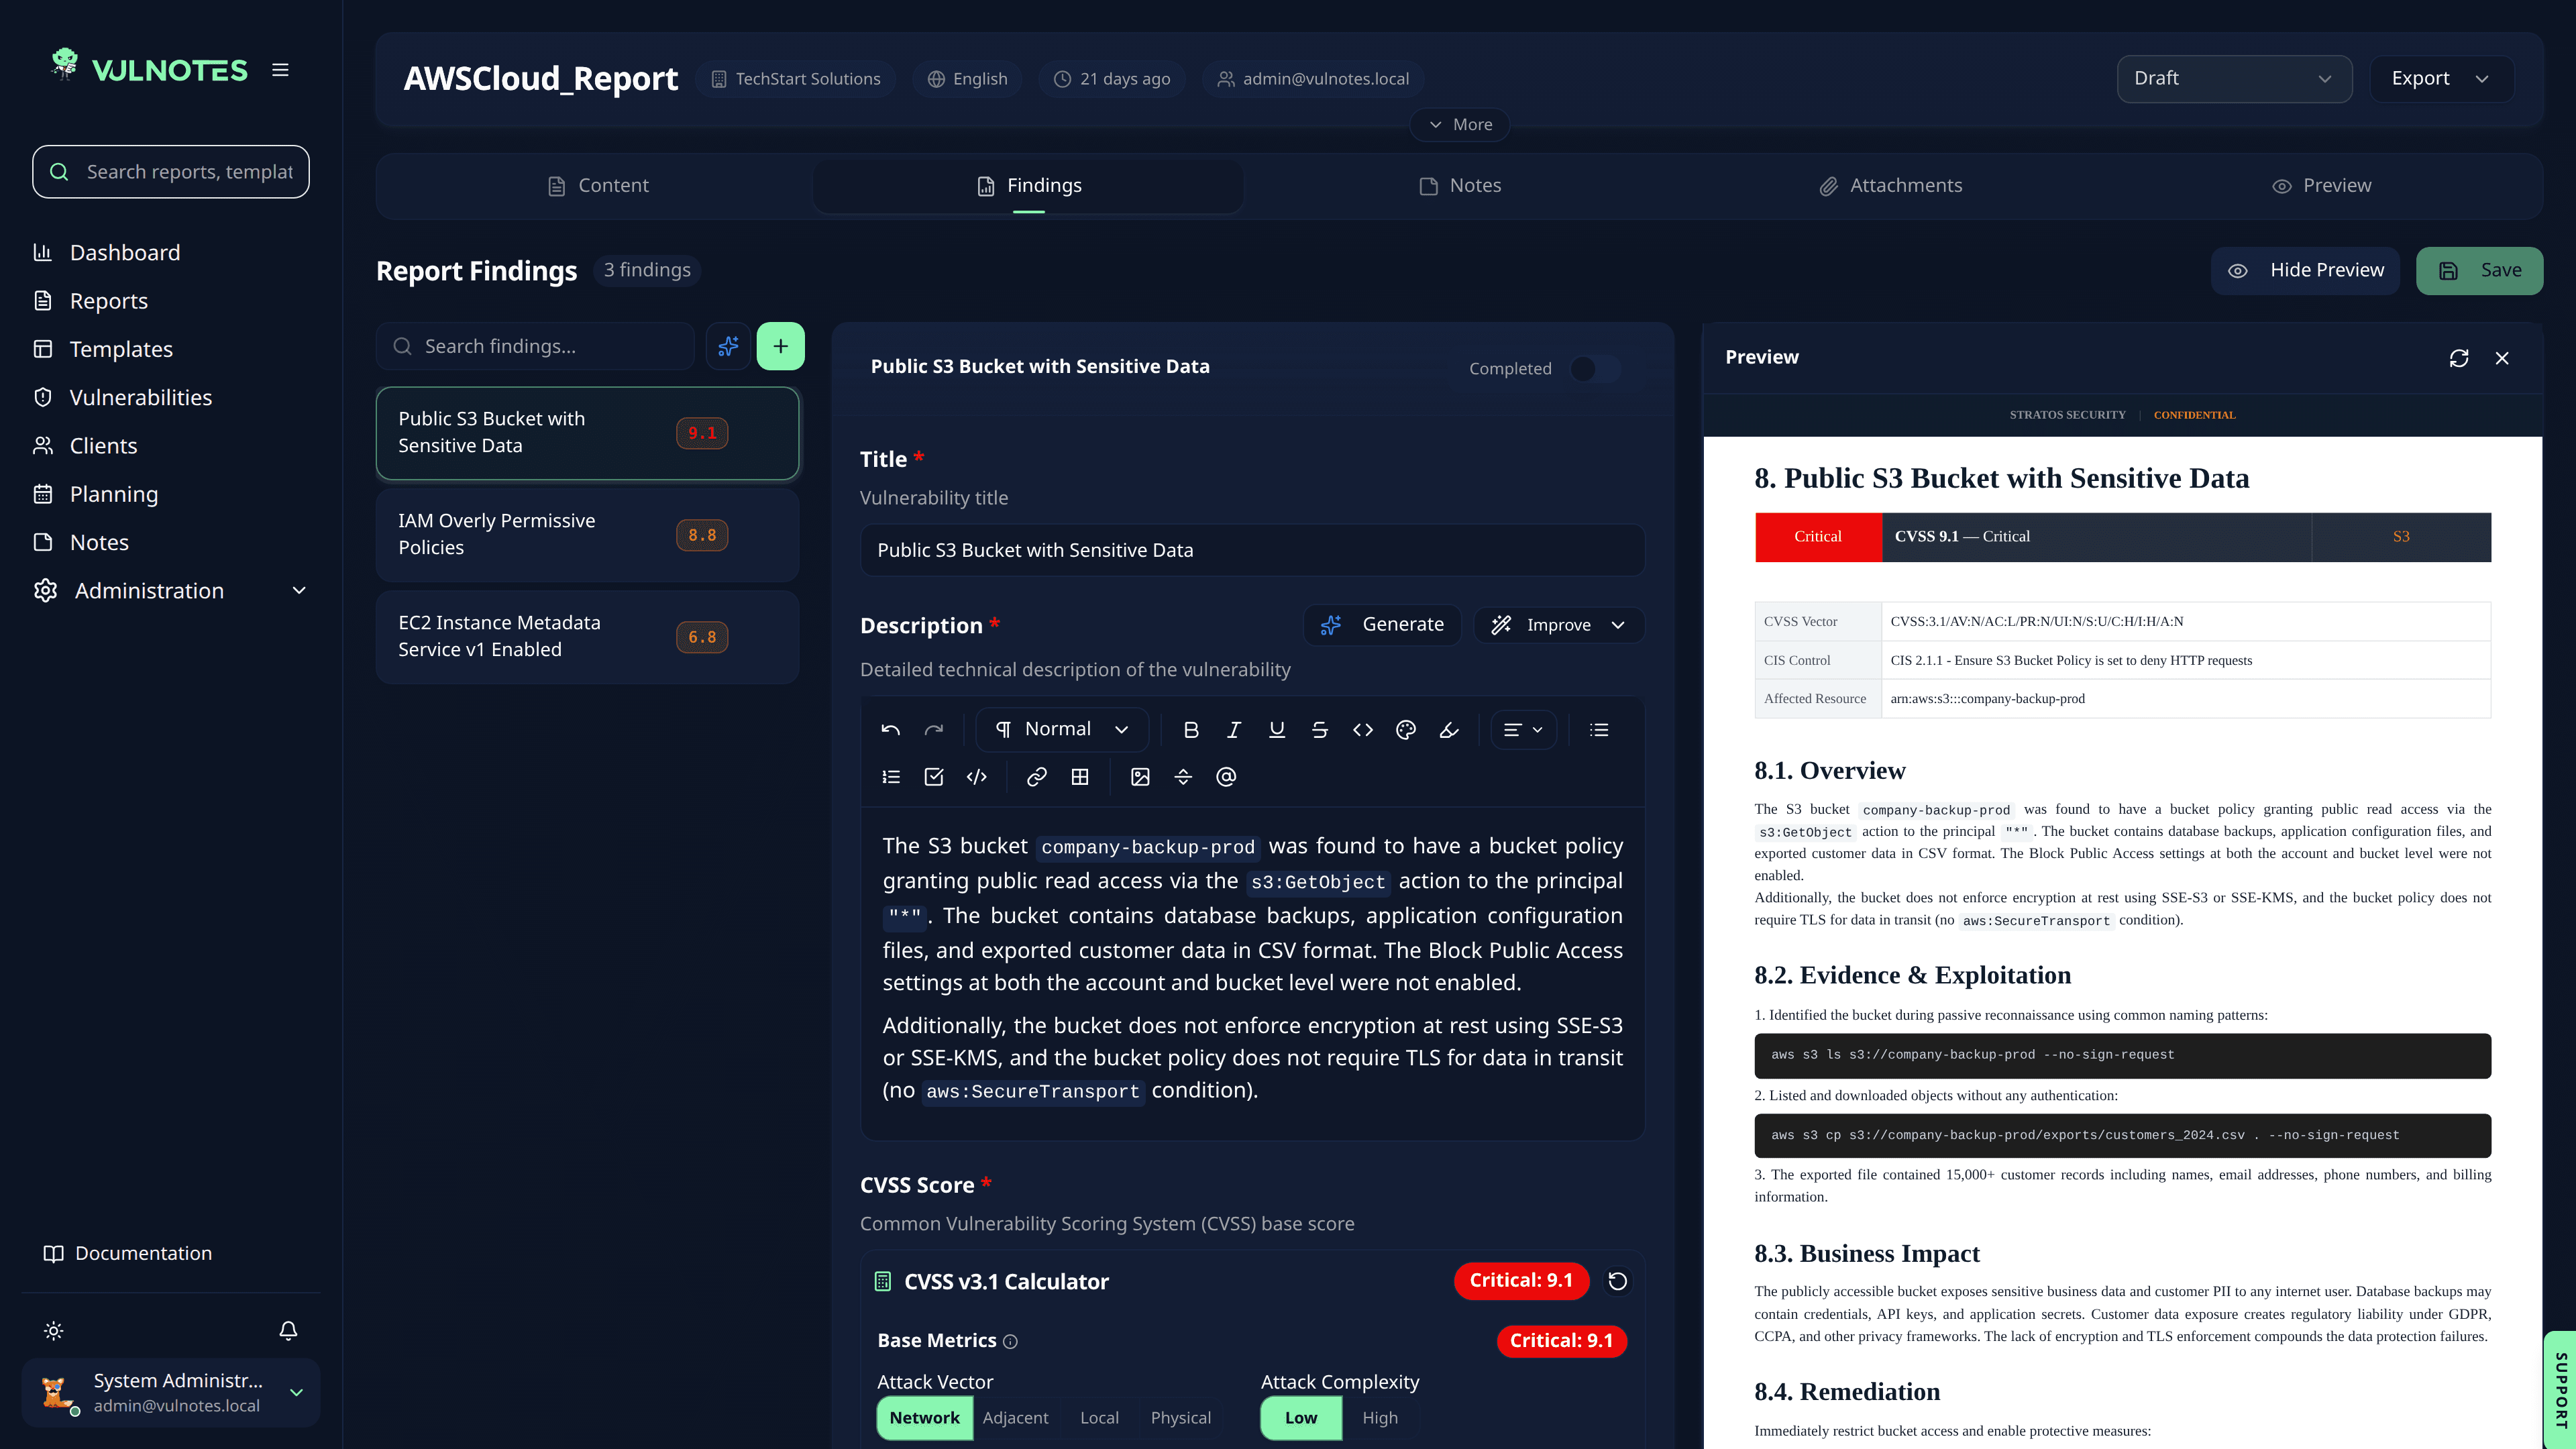
Looking for an AttackForge alternative built around the pentest report? Vulnotes lets your team import an existing Word report or design templates in a visual builder with live preview, write findings together in real time, review with snapshots and deliver DOCX, PDF, XLSX or JSON. Built-in EU-hosted AI, an MCP server and self-hosting are all part of one plan at €48 per user per month. AttackForge is a pentest management platform that generates reports from Word templates; here is how the two compare.
AttackForge information checked on 29 October 2026 against its public documentation and pricing. AttackForge is a trademark of AttackForge Pty Ltd.
Vulnotes vs AttackForge
- One simple per-user price
- Visual template builder
- Self-hosted at the SaaS price
Vulnotes or AttackForge: which one fits your team?
Vulnotes
Choose Vulnotes if…
- You want one price, €48 per user per month, with SSO, the REST API, the MCP server, built-in AI and self-hosting included and no limit on reports or projects.
- You would rather design report layouts in a drag-and-drop builder with a live paginated preview, or import your current Word report, than maintain tagged Word templates.
- Several testers write the same report and you want real-time co-editing with live cursors, then a snapshot-based review with change view and annotations.
- You need to self-host at the same price as the cloud, or run fully offline with the Air-Gap Server or Air-Gap Workstation editions.
- You want AI writing help inside the editor, from the EU-hosted Vulnotes AI or your own provider, including local models, with recognized sensitive data anonymized before each request.
AttackForge
Choose AttackForge if…
- You want one platform for the wider testing program, from project requests and scheduling to QA and retests.
- Your team prefers writing report templates in Word with tags.
- Your clients are used to working inside AttackForge and you want to keep that setup.
Vulnotes vs AttackForge: feature comparison
| Capability | Vulnotes | AttackForge |
|---|---|---|
| Pricing | Vulnotes€48 per user per month, monthly or annual billing, same price for SaaS and self-hosted | AttackForgeFrom $50 per month; Enterprise by quote |
| Plan limits | VulnotesPriced per user; all platform features in one plan; no limit on reports or projects | AttackForgePlans by number of testers and projects; extra project credits as paid top-ups |
| Report templates | VulnotesVisual drag-and-drop builder with live paginated preview; Word (.docx, .dotx) import | AttackForgeWord templates with ReportGen |
| Export formats | VulnotesPDF, DOCX, XLSX, JSON, password-protected ZIP | AttackForgeWord, PDF and JSON |
| Collaboration and review | VulnotesReal-time co-editing with live cursors; review snapshots with change view and annotations | AttackForgeTeam collaboration and QA workflow from the Team plan |
| Client portal | VulnotesWhite-label Client Portal add-on at €10 per user per month: 4 client companies per user, unlimited client users, remediation tracking and retest requests; Viewer Seats at €24 per month | AttackForgeClient role in the platform |
| Workflow and planning | VulnotesPlanning calendar with availability and conflict detection; kill chains; retests; pentest requests in the Client Portal | AttackForgeProject requests, scheduling and retests |
| Vulnerability library | VulnotesReusable multilingual library with custom vulnerability templates; CVSS 3.1, CVSS 4.0 or custom scoring | AttackForgePreloaded and custom libraries |
| Cloud hosting | VulnotesSaaS hosted in Europe by default or in another region on request | AttackForgeDedicated cloud tenant |
| Self-hosting | VulnotesDocker install, included at the same price as SaaS | AttackForgeEnterprise only |
| Air-gapped deployment | VulnotesAir-Gap Server and Air-Gap Workstation, offline licensing and signed updates, priced per deal | AttackForgeEnterprise Server, Enterprise only |
| AI | VulnotesBuilt-in EU-hosted Vulnotes AI (1M tokens per user per month) or your own provider, including local models; anonymization before each request; included in the plan | AttackForgeYour own assistant through MCP, an in-app upgrade except on SME and Enterprise |
| MCP server | VulnotesBuilt in, tools scoped by API key permissions; included in the plan | AttackForgeRemote and local MCP servers, an in-app upgrade except on SME and Enterprise |
| Import, API and automation | VulnotesDOCX/DOTX template import, standardized JSON import, PwnDoc importer, REST API, Python SDK and webhooks; Jira, GitHub Issues and Azure Boards from the Client Portal | AttackForgeTool imports; API and Flows (Jira, ServiceNow) as in-app upgrades except on SME and Enterprise |
| SSO and authentication | VulnotesMicrosoft Entra ID, Google, LDAP; enforced 2FA; included in the plan | AttackForgeSSO on Enterprise only; MFA |
AttackForge pricing vs Vulnotes: one per-user price, all core features included
Vulnotes has one plan: €48 per user per month, billed monthly or annually, at the same price for the SaaS and for a self-hosted install. The visual template builder, real-time co-editing, snapshot review, SSO with Google, Microsoft Entra ID or LDAP, the REST API, the MCP server and built-in AI are all part of it, and there is no limit on reports or projects. Two add-ons are optional: the Client Portal at €10 per user per month and Viewer Seats at €24 per month for read-only internal accounts.
AttackForge prices its plans by number of testers and projects, starting at $50 per month. Flows, the Self-Service API and AI MCP are included in the SME plan and are in-app upgrades on the other Core plans, extra project credits are bought as top-ups, and SSO is Enterprise only. With Vulnotes, a new tester is one more seat and a busy month of engagements never changes the bill, so a pentest team can plan its costs from headcount alone.
Co-editing, review and a white-label client portal
AttackForge is built around the wider testing program, from project requests and scheduling to QA and retests. Vulnotes focuses that effort on the report your client receives.
Several testers can write the same Vulnotes report at the same time, with live cursors and presence, and reviewers work from a snapshot that shows every change since it was taken, with annotations on the rendered pages. Around the report, Vulnotes covers engagement planning with availability and conflict detection, kill chains, retests and a reusable multilingual vulnerability library with CVSS 3.1, CVSS 4.0 or custom scoring.
When clients need more than the delivered report, the Client Portal add-on gives them a white-label space to track remediation, request retests and new pentests, and push findings to Jira, GitHub Issues or Azure Boards. Each Vulnotes user covers four client companies with unlimited client users.
A self-hosted AttackForge alternative at the same price as SaaS
AttackForge Core runs as a dedicated cloud tenant, and self-hosting, including air-gapped installs, is available with AttackForge Enterprise only.
Vulnotes runs as a SaaS, hosted in Europe by default or in another region on request, or as a self-hosted Docker install, both at €48 per user per month on monthly or annual billing, so even a small team can keep reports on its own infrastructure. For disconnected environments, the Air-Gap Server covers networks with no connectivity and the Air-Gap Workstation is a standalone desktop app for a single isolated machine, both with offline licensing and signed updates.
AI for pentest reports, with data anonymized before each request
AttackForge documents AI as connecting your own assistant to its data through MCP, which is included in the SME plan and Enterprise and an in-app upgrade on the other Core plans.
Vulnotes puts AI directly in the editor: drafting finding writeups, improving and translating report content, and turning a redacted screenshot into a finding. It uses the built-in EU-hosted Vulnotes AI, with 1M tokens per user per month included, or one of 12 provider types, including Ollama for local models and any OpenAI-compatible endpoint. Before each request, recognized client names, person names, emails, IP addresses, hostnames, scope entries and credential patterns are anonymized. An MCP server is included as well, so your own assistant can work with Vulnotes data within the permissions of its API key.
How to migrate from AttackForge to Vulnotes
Moving from AttackForge uses the Vulnotes DOCX template import for your ReportGen templates, the standardized JSON import for your writeup library, and the REST API or Python SDK for anything you want to automate.
- 1
Import your ReportGen templates
Upload your .docx templates under Templates > New Template > Import JSON or DOCX. Layout, headings, tables, charts and images become an editable template; replace the tags with Vulnotes variables and finding loops and check every page in the live preview.
- 2
Recreate your finding fields
Define vulnerability templates in Vulnotes that match the fields your writeups and findings use, then link them to your report templates.
- 3
Bring over your writeup library
Retrieve your writeups through the AttackForge Self-Service API and convert them to the Vulnotes standardized JSON import format, which also accepts clients and CVSS scores.
- 4
Set up clients and delivery
Create client companies and contacts, then decide whether clients need the Client Portal add-on or whether exported reports are enough. Viewer Seats cover internal read-only users.
- 5
Run one engagement in parallel
Deliver your next project in Vulnotes while past projects stay in your AttackForge exports.
Common questions
What is the best AttackForge alternative for pentest reporting?
It depends on what you want at the centre of your work. If it is the report, Vulnotes gives you a visual template builder with live preview, DOCX/DOTX import, real-time co-editing, snapshot review and DOCX, PDF, XLSX and JSON exports, with AI, the MCP server and self-hosting included at €48 per user per month.
How much does AttackForge cost?
AttackForge lists plans from $50 per month, with Enterprise pricing by quote; SSO is Enterprise only, and Flows, the API and AI MCP are in-app upgrades on Core plans other than SME. Vulnotes is €48 per user per month, billed monthly or annually, at the same price for SaaS and self-hosted, with all platform features in one plan and a 14-day trial when you schedule a demo.
AttackForge vs Vulnotes: which is better for pentest reports?
AttackForge covers the wider testing program and generates reports from tagged Word templates. Vulnotes is built around writing and delivering the report: templates are designed visually with a live paginated preview, testers co-edit in real time, and reviewers work from snapshots with a change view and annotations.
How do I migrate from AttackForge to Vulnotes?
Import your ReportGen .docx templates into the Vulnotes template builder and replace the tags with variables and finding loops. Then bring your writeup library over through the standardized JSON import, and automate the rest with the REST API or Python SDK.
Can I reuse my AttackForge ReportGen templates in Vulnotes?
Yes. Vulnotes imports .docx and .dotx files and converts text, headings, lists, tables, charts and images into an editable template. ReportGen tags come through as plain text, and you replace them with Vulnotes variables and finding loops in the visual builder.
Is there a self-hosted AttackForge alternative?
AttackForge offers self-hosting only with its Enterprise edition. Vulnotes includes a self-hosted Docker install in its standard plan, at the same €48 per user per month as the SaaS, and offers Air-Gap Server and Air-Gap Workstation editions for offline environments.
Does Vulnotes have AI features like AttackForge?
AttackForge documents AI as connecting your own assistant through MCP, an in-app upgrade on Core plans other than SME. Vulnotes includes an MCP server too, and also builds AI into the editor: the EU-hosted Vulnotes AI with 1M tokens per user per month, or your own provider including local models, with recognized sensitive data anonymized before each request.
Can my clients follow findings in Vulnotes?
Yes, with the Client Portal add-on at €10 per user per month. Clients get a white-label space to track remediation, request retests and new pentests, and push findings to Jira, GitHub Issues or Azure Boards, with four client companies per Vulnotes user and unlimited client users.
See your own report
in Vulnotes.
Set up in minutes. Write, review and deliver your next pentest report in Vulnotes.